Quick Safety Checklist
| Threat | Primary Defense |
|---|---|
| Unauthorized linked device | Regularly check “Linked Devices” on your phone |
| Fake login QR code | Only scan QR codes at web.whatsapp.com |
| Phishing via Google Ads | Avoid “Sponsored” search results for WhatsApp |
| Logged in on public PC | Always click “Log out” before closing the tab |
WhatsApp Web’s “Multi-Device” feature is incredibly convenient, but it also opens up a specific security vulnerability known as “Session Hijacking.” Because a device remains logged in even if your phone is offline, an attacker who gains access to your active web session—either physically or via a malicious link—can read your messages and scam your contacts without you ever knowing.
Fortunately, Meta has built multiple layers of defense into WhatsApp. Here is how to audit your account, identify potential hijacking, and secure your WhatsApp Web session for good.
1. Audit Your Linked Devices Frequently
This is your first and most powerful line of defense. Every device currently logged in to your WhatsApp account is listed on your primary phone.
- Open WhatsApp on your mobile phone.
- Go to Settings > Linked Devices.
- Look for any device you don’t recognize (e.g., a “Linux” computer if you use Windows, or a login from a city you haven’t visited).
- Tap the suspicious device and select Log Out. This kills the attacker’s session immediately.
2. Beware of “QR Code Phishing”
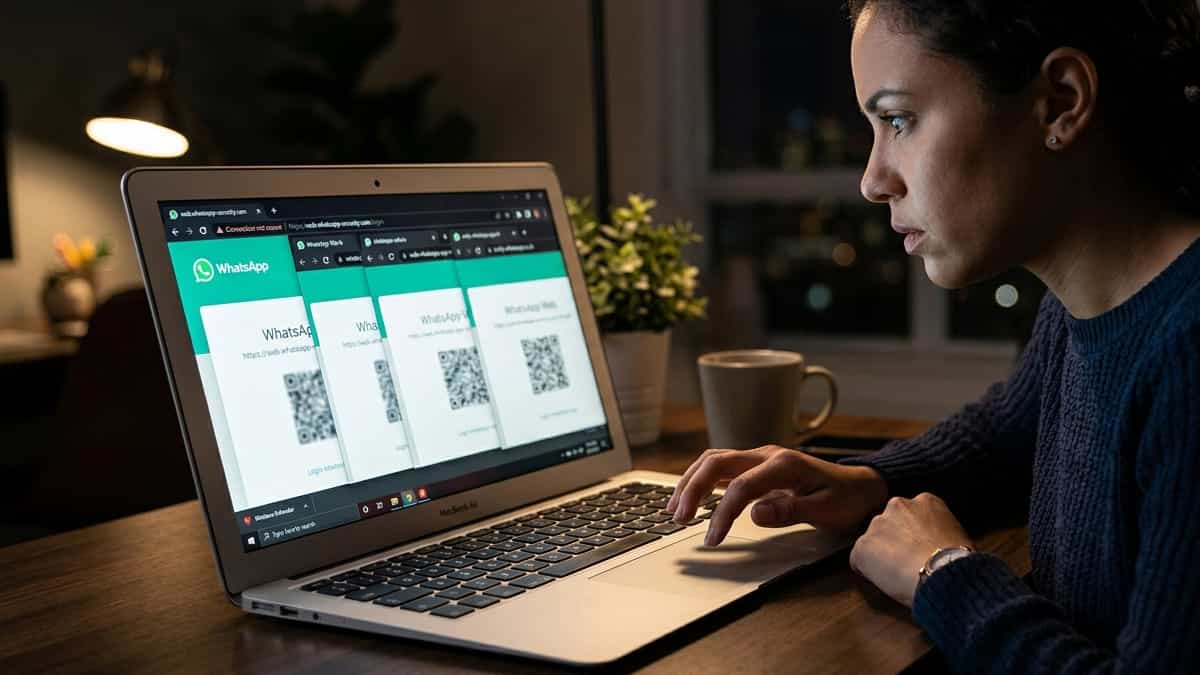
A common scam involves attackers sending you a link to a website that looks like WhatsApp Web but is actually a proxy. When you scan the QR code on the fake site, you aren’t logging in to your own computer; you’re giving the attacker full access to your account on *their* computer.
- Golden Rule: Only scan a QR code if the URL in your browser’s address bar is exactly
web.whatsapp.com. - Check for the padlock: Ensure the site has a valid SSL certificate issued to WhatsApp LLC.
3. Enable Biometric “App Lock” on Your Phone
WhatsApp now requires you to unlock your phone’s biometric security (FaceID or Fingerprint) before you are allowed to link a new device to your web account. This prevents anyone who physically grabs your phone from quickly scanning a QR code to hijack your session.
- Ensure you have Fingerprint/Face Lock enabled in your phone’s WhatsApp settings (Settings > Privacy > App Lock).
- If someone tries to link a device without your face or finger, the process will fail.
4. Avoid Public and Shared Computers
If you must use WhatsApp Web on a public computer (hotel business center, library, etc.), follow the “two-step exit” rule:
- Manual Logout: Click the three dots (…) at the top of the chat list and select Log out.
- Incognito Mode: Always use an Incognito or Private window on a public PC. This ensures your cookies and session data are wiped the moment the window is closed.
5. Set Up Two-Step Verification (MFA)
While Two-Step Verification (a 6-digit PIN) is primarily for re-registering your phone number, it also acts as a secondary “gate” for web sessions. Sometimes, WhatsApp will ask for your PIN on the web client as a secondary security check. Without the PIN, the hacker cannot proceed.
- Go to Settings > Account > Two-step verification on your phone to set it up.
6. Use the Screen Lock Feature (Desktop App)
If you use the official WhatsApp Desktop app for Windows or Mac, you can set a separate password for the app itself. Even if someone gains physical access to your computer, they can’t open your chats without that specific password.
- Click the Gear icon (Settings) in the app.
- Select Privacy > Screen Lock.
- Set your password and choose how quickly it should lock (e.g., after 1 minute of inactivity).
Your privacy is your responsibility. By auditing your linked devices and being vigilant about where you scan QR codes, you can successfully prevent session hijacking and keep your personal conversations private. If you ever suspect your account has been compromised, your first move should always be to “Log out from all devices” on your mobile phone.