If you run a website—whether a personal blog, a business site, or an e‑commerce store—you’ve probably heard the term SSL certificate. It’s the little padlock icon in the browser’s address bar, and it’s essential for encrypting data and building trust with your visitors.
But when you go to buy an SSL certificate, you’re faced with choices like DV, OV, EV, Wildcard, Multi‑Domain… It can quickly become overwhelming.
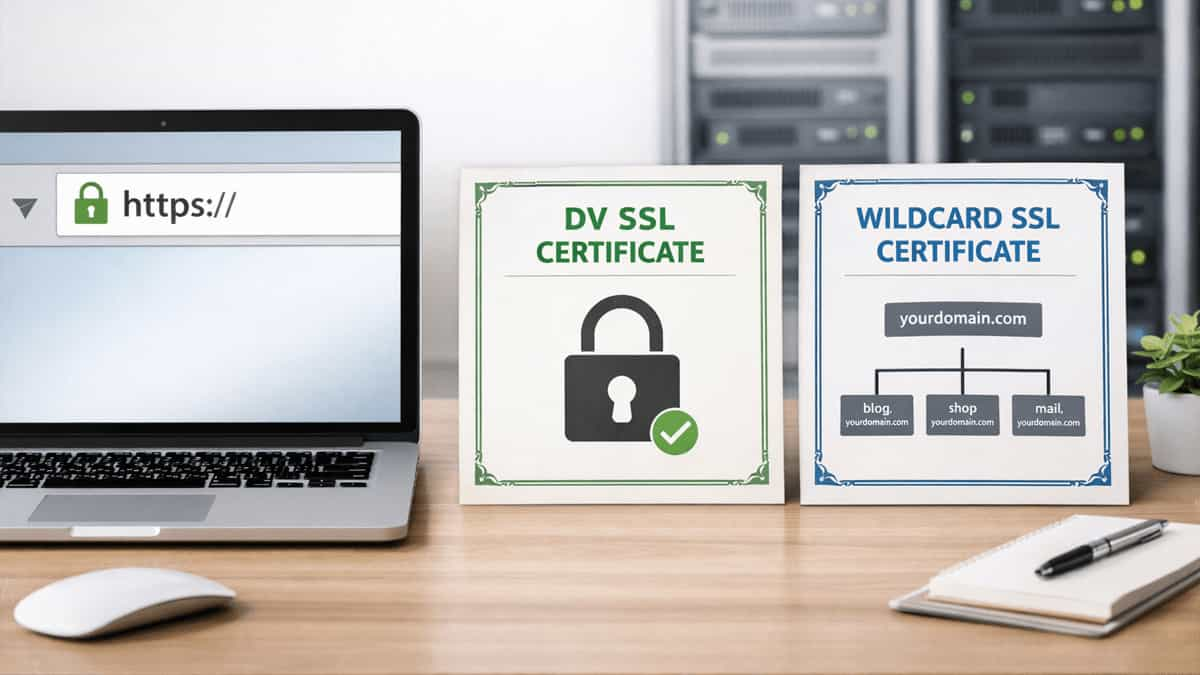
Two of the most frequently compared options are DV SSL (Domain Validation) and Wildcard SSL. While they serve very different purposes, many website owners aren’t sure which one fits their needs.
This guide will walk you through everything you need to know—from the basics to advanced comparisons, common myths, and real‑world scenarios—so you can make an informed decision.
Table of Contents
What is an SSL Certificate?
SSL (Secure Sockets Layer) and its successor TLS (Transport Layer Security) are cryptographic protocols that encrypt data between a user’s browser and the server hosting your website. When you install an SSL certificate, your site’s traffic is secured, and you get the coveted HTTPS prefix.
Beyond security, SSL certificates also:
- Boost SEO (Google gives preference to HTTPS sites)
- Increase visitor trust (no “Not Secure” warnings)
- Protect sensitive data (passwords, credit card info, personal details)
All SSL certificates are issued by a Certificate Authority (CA) after some level of validation. The main differences between certificate types lie in how much validation is performed and how many domains/subdomains are covered.
Understanding DV SSL (Domain Validation)
Domain Validation (DV) is the most basic and fastest type of SSL certificate. The CA only verifies that you have control over the domain name—usually by clicking a link sent via email or adding a DNS TXT record.
Key Characteristics
- Validation time: Minutes to hours
- Validation level: Domain ownership only
- Cost: Free (e.g., Let’s Encrypt) to very low
- Trust indicators: Padlock icon only (no green bar or company name)
- Best for: Blogs, personal sites, test environments, and any site that doesn’t handle sensitive customer data
Pros
- Quick and easy to obtain
- Often free (Let’s Encrypt, Cloudflare)
- Provides the same encryption strength as more expensive certificates
Cons
- Does not verify the identity of the organization behind the site
- Low trust for e‑commerce or financial services
Understanding Wildcard SSL
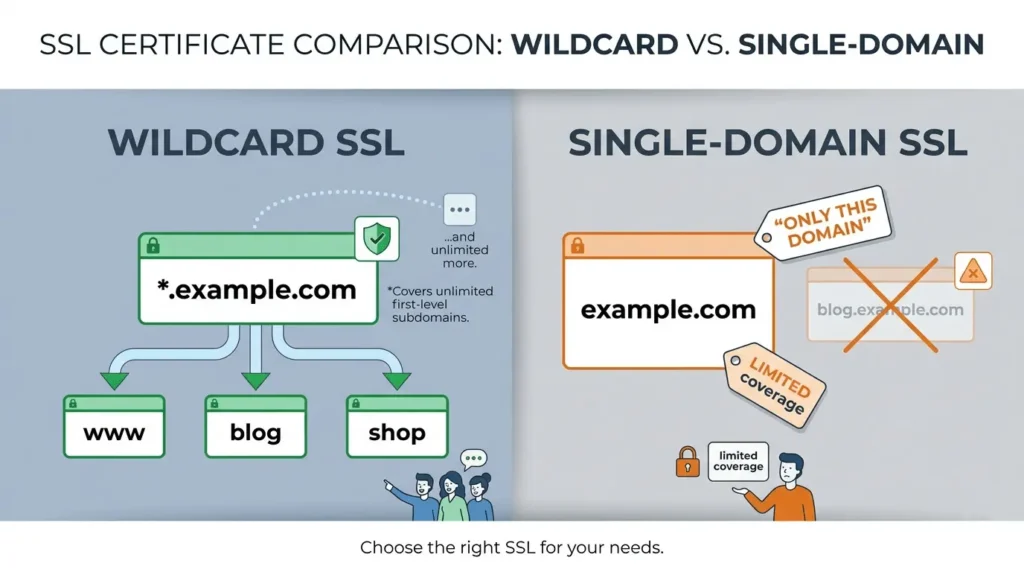
A Wildcard SSL certificate secures your primary domain and all its first‑level subdomains (unlimited subdomains) with a single certificate. For example, a Wildcard for *.example.com covers:
www.example.comblog.example.comshop.example.commail.example.com
Key Characteristics
- Validation level: Usually Domain Validation (DV) or Organization Validation (OV) – Wildcard OV is common for business
- Coverage: One domain + unlimited first‑level subdomains
- Cost: Significantly more than a single‑domain DV certificate
- Best for: Sites with multiple subdomains, e.g., SaaS platforms, agencies, or any business with a complex subdomain structure
Pros
- Cost‑effective if you have many subdomains (cheaper than buying separate certs)
- Easy to manage – one certificate, one renewal date
- Available with higher validation levels (OV) for added trust
Cons
- More expensive upfront than a single‑domain DV
- Does not cover second‑level subdomains (e.g.,
admin.blog.example.comwould need another cert or a multi‑level wildcard, which is rare) - If the private key is compromised, all subdomains are affected
DV SSL vs. Wildcard SSL: Feature Comparison
| Feature | DV SSL | Wildcard SSL |
|---|---|---|
| Validation Type | Domain only (DV) | Usually DV or OV (Wildcard OV is common) |
| Coverage | Single domain (e.g., example.com) | Primary domain + unlimited first‑level subdomains |
| Validation Time | Minutes to hours | DV: hours; OV: 1–3 days |
| Cost | Free – $30/year | $100 – $500+/year (depends on provider and validation level) |
| Trust Indicators | Padlock only | Padlock only (DV) or company name in certificate (OV) |
| Best For | Personal sites, blogs, internal tools | Businesses, SaaS, e‑commerce with subdomains |
| Renewal | Simple | Single renewal for all subdomains |
| Issuance Flexibility | Easy to automate (e.g., Let’s Encrypt) | Requires manual validation or ACME with some providers |
Common Myths About DV and Wildcard SSL
Myth 1: “DV SSL is insecure”
Fact: Encryption strength (256‑bit, RSA 2048/ECC) is the same across all SSL types. DV certs use the same encryption as EV certs. The only difference is the level of identity verification.
Myth 2: “I can get an EV Wildcard for unlimited subdomains”
Fact: While you can get an EV Multi‑Domain SSL (which requires you to list every subdomain individually), a true Wildcard (using the * symbol for unlimited, future subdomains) is restricted to DV or OV validation only. Industry standards (CA/B Forum) do not allow Extended Validation on a true wildcard certificate because the subdomains are not pre‑identified.
Myth 3: “A Wildcard SSL secures all my subdomains automatically”
Fact: It covers only first‑level subdomains. sub.sub.example.com requires a separate certificate or a multi‑domain wildcard (rare).
Myth 4: “Wildcard SSL is only for large enterprises”
Fact: If you run a blog with a separate subdomain for a shop or a forum, a wildcard can be cost‑effective even for small businesses.
Myth 5: “I need an EV SSL to accept payments”
Fact: PCI DSS requirements only mandate strong encryption—any DV or OV cert is acceptable. EV is optional for extra trust.
Myth 6: “Free SSL (Let’s Encrypt) is not trusted by browsers”
Fact: Let’s Encrypt is a trusted CA, and its certificates are accepted by all major browsers. The only drawback is they are DV only and renew every 90 days (can be automated). In fact, the industry is moving toward 90‑day certificates as the norm to encourage automation and improve security.
Personal vs. Enterprise: Which SSL Suits Your Project?
| Use Case | Recommended SSL |
|---|---|
| Personal blog / portfolio | Free DV SSL (Let’s Encrypt) – secure, simple, and zero cost. |
| Small business with one domain | Single‑domain OV SSL – gives a company name in the certificate for credibility. |
| Small business with multiple subdomains | Wildcard OV SSL – covers all subdomains and shows business validation. |
| E‑commerce store | OV SSL (or EV Multi‑Domain if you need strong branding on specific subdomains). Ensure the certificate supports the domain and any subdomains like checkout. or secure. |
| SaaS platform (multi‑tenant) | Wildcard OV SSL to cover app.yourplatform.com, api.yourplatform.com, etc. |
| Large enterprise / financial | EV Multi‑Domain SSL for the highest level of validation on specific, pre‑defined subdomains. |
Personal vs. Enterprise Key Takeaway:
- Personal: DV is almost always sufficient.
- Business: OV or Wildcard OV is recommended for customer trust.
- Enterprise: Consider EV Multi‑Domain if you need the green‑bar trust (though browsers are phasing out the visible address bar indication) on explicitly listed subdomains.
Popular SSL Providers at a Glance (Updated)
| Provider | DV | Wildcard DV | Wildcard OV | EV Multi‑Domain | Notes |
|---|---|---|---|---|---|
| Let’s Encrypt | Free | Free | ❌ | ❌ | Automated, 90‑day renewal; ideal for tech‑savvy users |
| Cloudflare | Free (via origin certs) | Free (if using Cloudflare proxy) | ❌ | ❌ | Best if you use Cloudflare’s CDN |
| GoDaddy | ✓ (paid) | ✓ | ✓ | ✓ | Popular for domain/hosting bundles; offers easy installation via cPanel; supports EV Multi‑Domain |
| Sectigo (formerly Comodo) | Low cost | ✓ | ✓ | ✓ | Popular choice, easy to purchase |
| DigiCert | ✓ | ✓ | ✓ | ✓ | High‑trust, enterprise‑focused (expensive) |
| GlobalSign | ✓ | ✓ | ✓ | ✓ | Another premium enterprise CA |
| Namecheap / SSLs.com | Resellers of Sectigo/DigiCert; competitive pricing | ✓ | ✓ | ✓ | Good for budget‑conscious buyers; offers EV Multi‑Domain |
Forward‑Looking Note: The industry is moving toward shorter certificate lifetimes (90 days is becoming the new norm) to improve security and encourage automation. Many CAs are also starting to offer Post‑Quantum Cryptography (PQC) readiness—a future‑proofing feature that ensures your certificates remain secure against quantum‑computer attacks.
Frequently Asked Questions (Doubts & Answers)
Q1: Can I use a Wildcard SSL on a shared hosting account?
Yes. Most shared hosting panels (cPanel, Plesk) support wildcard certificates, but you must ensure the hosting provider allows custom SSL installation.
Q2: Do I need a dedicated IP for SSL?
No. SNI (Server Name Indication) technology allows multiple SSL certificates to be served from a single IP. All modern browsers and hosting environments support SNI.
Q3: Can I upgrade a DV certificate to a Wildcard later?
No. Each certificate type is issued separately. You would need to purchase a new Wildcard certificate and replace the old one.
Q4: What’s the difference between Wildcard and Multi‑Domain (SAN) SSL?
- Wildcard: Covers one domain + all its first‑level subdomains (unlimited, but unnamed).
- Multi‑Domain (SAN): Covers multiple specific domain names (e.g.,
example.com,example.org,example.net) with one certificate. Some certificates combine both (e.g., a SAN certificate that also includes wildcards for a subset of the names).
Q5: Is a Wildcard SSL available in EV?
Short Answer: No. Industry standards (CA/B Forum) do not allow a “true Wildcard” (*.domain.com) to have Extended Validation.
The Alternative: If you need the highest level of validation on multiple subdomains, you should buy an EV Multi‑Domain SSL. This gives you EV trust on each explicitly listed subdomain, but you must list every subdomain when you purchase the certificate—adding a new subdomain later requires reissuance.
Q6: Does a Wildcard SSL protect against subdomain takeover?
No. SSL only encrypts traffic. Subdomain takeover is a DNS / hosting security issue. Always secure unused subdomains properly.
Q7: My site uses www and non‑www. Do I need a wildcard?
No. A standard single‑domain certificate can cover both example.com and www.example.com if you include the www variant as a Subject Alternative Name (SAN). This is a cost‑saving tip—buy a wildcard only if you actually need other subdomains like blog.example.com.
Final Conclusion
Choosing between DV SSL and Wildcard SSL comes down to two questions:
- How many subdomains do you need to secure?
- Only
wwwand the bare domain → Single‑domain DV or OV is enough. - Many subdomains → Wildcard is your most cost‑effective and manageable choice.
- What level of trust does your audience expect?
- Personal projects / internal tools → DV is perfectly fine.
- Business / e‑commerce → OV (or Wildcard OV) builds credibility.
For most site owners, starting with a free DV SSL (like Let’s Encrypt) is the smartest move. As your site grows and you add subdomains, upgrading to a Wildcard OV provides the perfect balance of coverage and trust without breaking the bank.
Once your SSL is secured, ensuring your cloud hosting environment is optimized for HTTPS delivery is the next step for a fast, secure site.
If you’re still unsure which SSL is right for your project, start with a free DV certificate—you can always upgrade later without disrupting your site. For businesses managing multiple subdomains, a Wildcard OV is the industry standard that balances cost, convenience, and customer trust. And if you need the highest level of validation on specific subdomains, an EV Multi‑Domain SSL is the way to go.